Microsoft Purview
Data governance, information protection, compliance, insider-risk and data-loss-prevention capabilities across Microsoft data estates.
Technical Overview
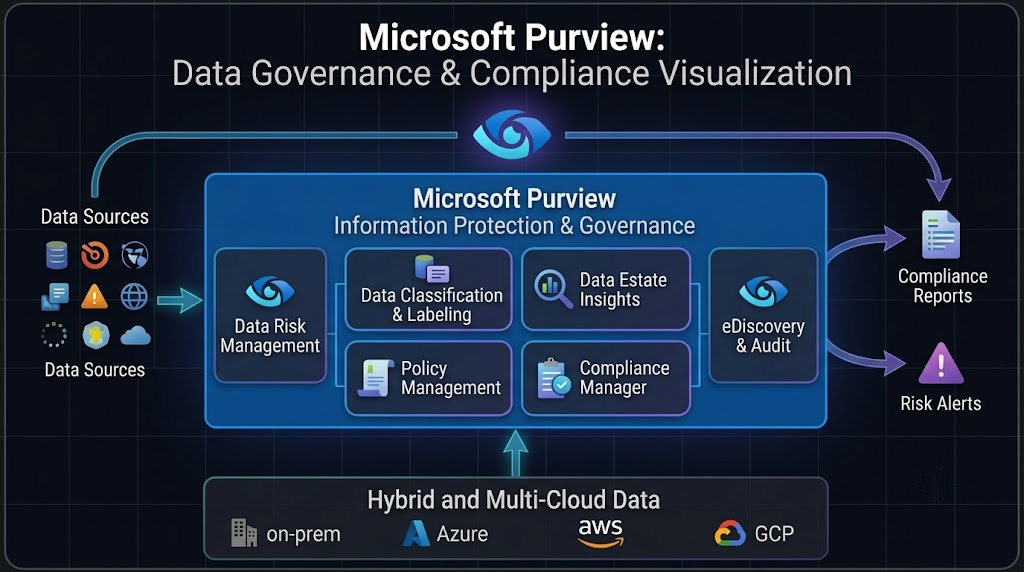
Microsoft Purview is a portfolio for data security, data governance and compliance across Microsoft 365, Azure, multicloud and on-premises data. It helps organisations discover, classify, protect and govern data through its lifecycle.
Core solutions include Information Protection (sensitivity labels), Data Loss Prevention, Insider Risk Management, Data Lifecycle Management, eDiscovery and Audit, Compliance Manager and the Unified Catalog for governance.
How Microsoft Purview works
A five-step technical flow.
Technical architecture
Operating flow of Microsoft Purview from onboarding to outcome.
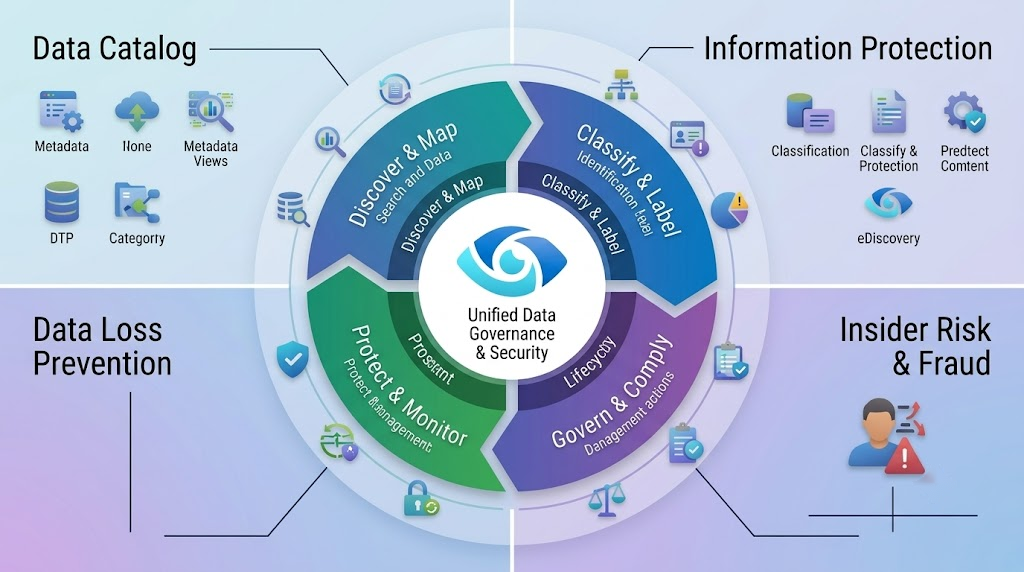
- 01DiscoverScan and inventory data across Microsoft 365, Azure and other sources.
- 02ClassifyApply sensitive info types, classifiers and sensitivity labels.
- 03ProtectEnforce encryption, access and DLP policy on labelled data.
- 04MonitorAudit, alerts and insider risk signals reveal misuse.
- 05GovernRetention, records and catalog policies manage the lifecycle.
Discover → Classify → Protect → Monitor → Govern
Core Capabilities
Purview provides built-in and custom sensitive information types, trainable classifiers, sensitivity labels with encryption and markings, DLP policies for endpoints, email and cloud apps, retention labels and records management, communication compliance, audit search, and data maps and lineage for governance.
Integrations
Purview works with Microsoft 365 apps, SharePoint and OneDrive, Exchange, Teams, Microsoft Entra ID, Intune, Defender for Endpoint and Defender for Cloud Apps. Purview signals can also feed Microsoft Defender XDR and Sentinel, and the Data Map can scan Azure, AWS, SQL and other supported sources.
Key benefits
Main outcomes you can expect.
- 01Know Your DataFind where sensitive information lives.
- 02Consistent ProtectionLabels and DLP follow the data.
- 03Audit ReadinessEvidence and reports support compliance reviews.
- 04Reduced RiskDetect and limit leakage and insider misuse.
Implementation Approach
We start with a data and compliance assessment, define a label taxonomy and classification rules, then pilot labels and DLP in audit mode. Policies are tuned from real activity before enforcement, followed by retention, insider risk and eDiscovery setup, user guidance and admin handover.
Operational & Security Considerations
Features depend on the Microsoft 365 licence tier (for example E3 versus E5 Compliance). Start policies in simulation or audit mode, involve legal and HR before insider risk or communication compliance, and document label ownership, exceptions and review cycles.
How ISS Technologies Helps
ISS Technologies assesses your environment, implements and integrates Microsoft Purview, and supports your team in day-to-day operations. Related service: Data Loss Prevention.